ZNetLab › Published › Question
Ping works, SSH hangs — only over the site-to-site VPN
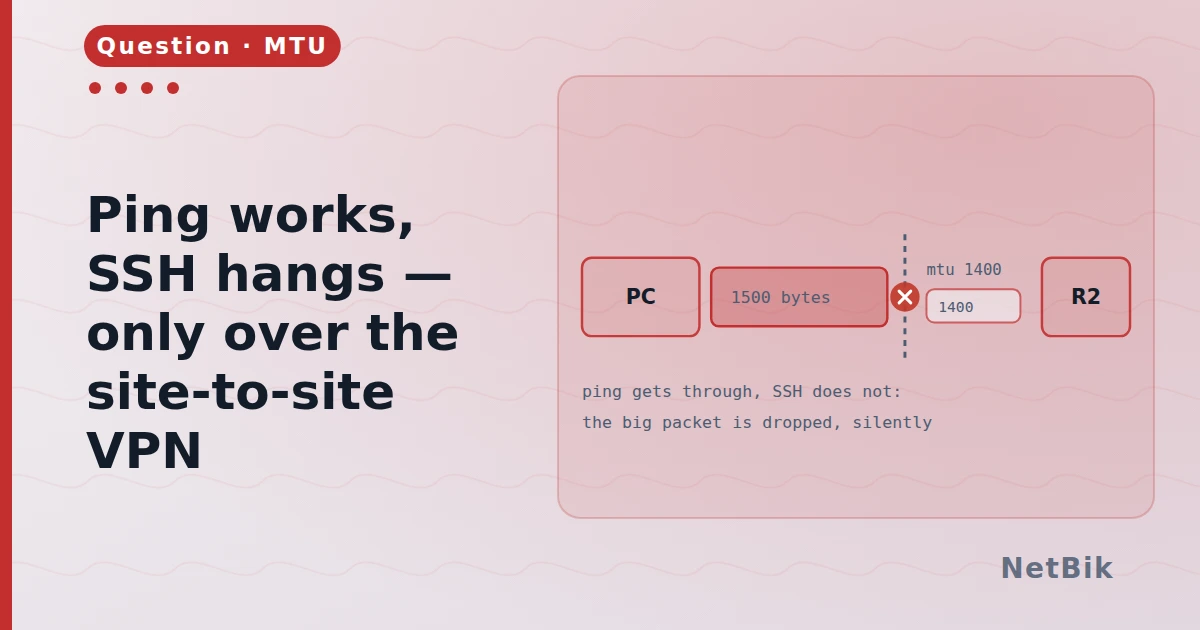
Site-to-site IPsec between two branches. Ping across it works, DNS works, and SSH connects, shows the banner, and then freezes. Same with any HTTPS page that is not tiny. It only happens over the tunnel — the same servers are fine from inside the site.
No drops counted on either firewall, nothing in the IPsec logs.
1 answer
@admin · 2026-10-09
That is an MTU black hole, and the "no drops counted" is part of the signature — the drop happens at a device in the middle that you are not looking at.
IPsec adds overhead, so the effective MTU across the tunnel is lower than 1500. TCP sets the Don't Fragment bit, so the oversized packet is dropped and an ICMP "fragmentation needed" is sent back. If anything on the path blocks ICMP — and most hardening guides tell people to — the sender never finds out and just retransmits the same packet for ever. Small things get through; large ones vanish. SSH connects on small packets and hangs on the first big one.
Confirm it:
C:\> ping 10.2.0.9 -f -l 1472
Packet needs to be fragmented but DF set.
Then walk the size down until it passes. The size that works plus 28 is your real path MTU.
The quickest fix that does not need anybody else's cooperation is to clamp the TCP MSS on the tunnel interface:
R1(config)# interface Tunnel0
R1(config-if)# ip tcp adjust-mss 1360
This rewrites the MSS during the TCP handshake, so the two ends agree never to send anything too large and PMTUD is never needed. Note it only helps TCP — if UDP applications break across the same tunnel later, this is why.
The correct fix is to permit ICMP type 3 code 4 on the path.
Can you answer this?
Replies, likes and bookmarks live in the community half, which needs a free account. Writing here is free too, and everything is reviewed before it is published.
Open this in the communityEverything publishedHow this works